Auth for MCP

Ship your MCP server.
Not an OAuth implementation.

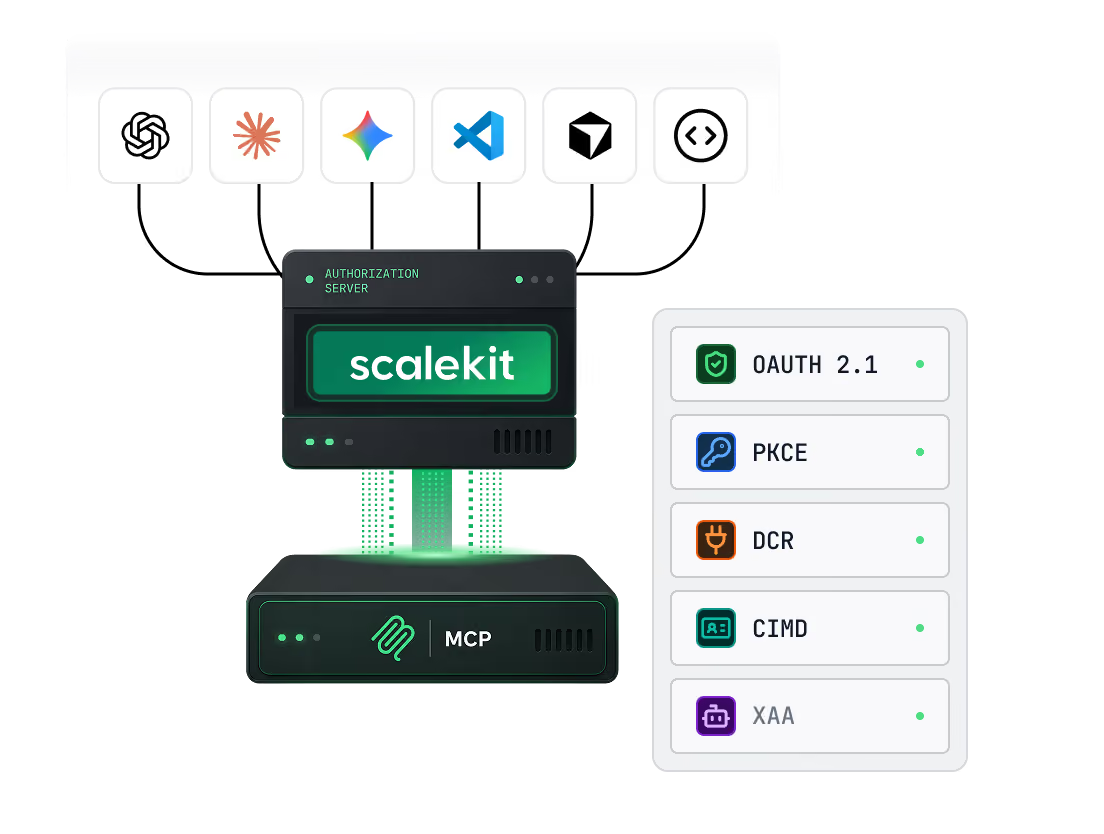
Drop-in OAuth 2.1 for any MCP server. Bring your existing auth — users connect from Claude, ChatGPT, and Cursor in days.
Bring your own auth

Your existing auth stays.
Exactly as it is

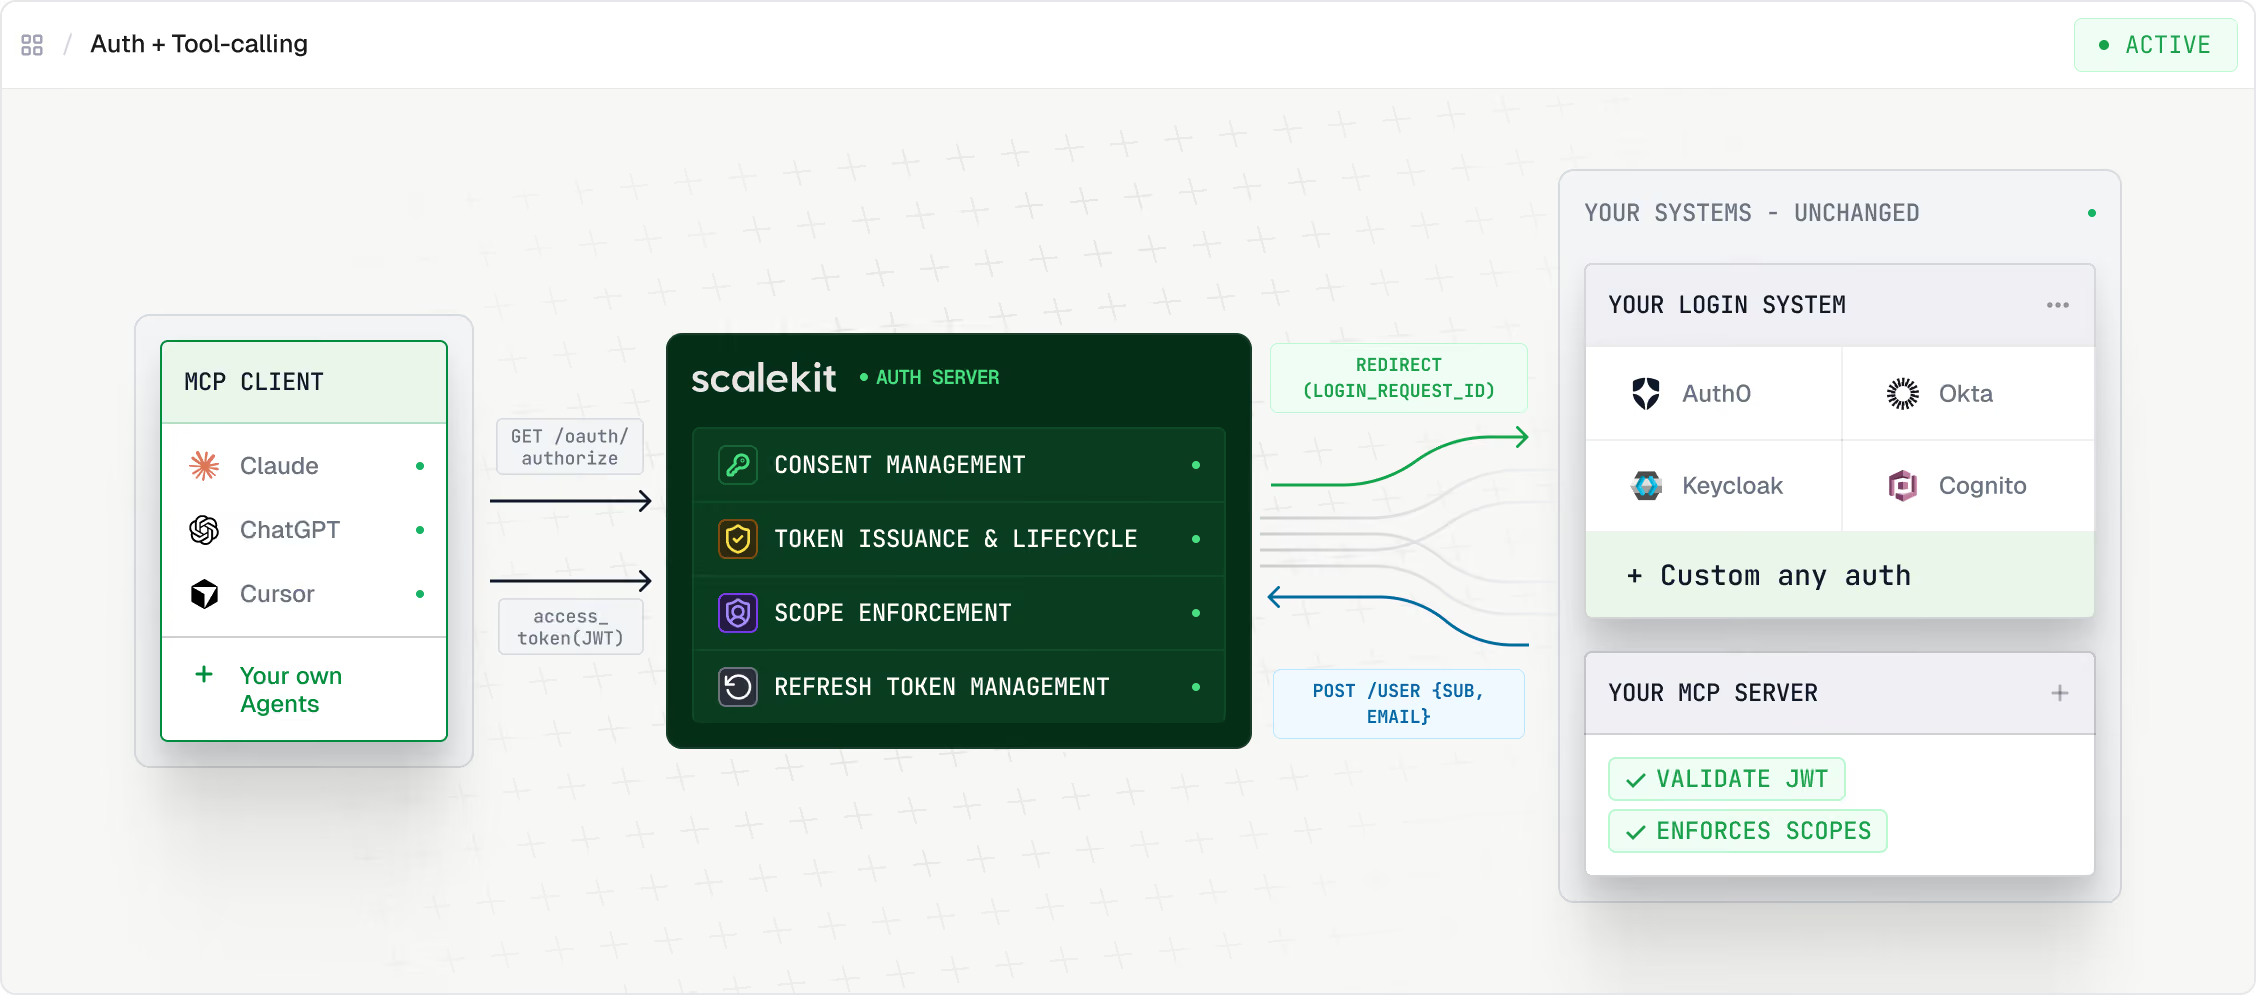
Don't migrate users. Don't rebuild your login flow. Scalekit is the OAuth layer — your existing system handles identity.
01
Redirect to your login
Any auth request is sent to your existing login page — unchanged.
02
Your system authenticates
SSO, password, magic link — whatever you already run.
03
Return sub. Get token.
One backend call. Scalekit handles consent, token lifecycle, and refresh.
Works with
System authenticates
Enterprise

Make your MCP server
XAA-ready.

Cross-App Access lets your customers' enterprise IdPs authorize agents directly. Admins configure once — no per-user OAuth flows, no long-lived keys.
Agents present a signed identity assertion from their IdP. Scalekit exchanges it for a short-lived, scoped token.
Admin configures once. All users in mapped groups inherit access automatically.
Every token request logged through the IdP's existing audit trail — one control plane for all agent access.
CUSTOMERS

Teams shipping MCP to production.

Our customers wanted to work inside Claude and Cursor, not just inside Rocketlane. Scalekit let us meet them there: live in days, EU residency built in, nothing rebuilt in our own auth stack.
Deepak Bala
CTO & Co-founder, Rocketlane
“I wanted to get the OAuth layer done without burning a full sprint rebuilding infrastructure we'd already built. Scalekit let us add auth to the existing server, configure the right permissions per tool from a dashboard, and move on. We didn't have to migrate to a new framework or touch the core logic.”
Kartikay Dhar
Director of Product, AI · Sprouts.ai
We wanted our users to be able to ask their AI tools the same questions they'd ask Brand24 directly. Scalekit let us ship that without turning our engineering team into OAuth specialists.
Bartłomiej Krupa
Developer, Brand24
Our customers wanted to work inside Claude and Cursor, not just inside Rocketlane. Scalekit let us meet them there: live in days, EU residency built in, nothing rebuilt in our own auth stack.
Deepak Bala
CTO & Co-founder, Rocketlane
“I wanted to get the OAuth layer done without burning a full sprint rebuilding infrastructure we'd already built. Scalekit let us add auth to the existing server, configure the right permissions per tool from a dashboard, and move on. We didn't have to migrate to a new framework or touch the core logic.”
Kartikay Dhar
Director of Product, AI · Sprouts.ai
We wanted our users to be able to ask their AI tools the same questions they'd ask Brand24 directly. Scalekit let us ship that without turning our engineering team into OAuth specialists.
Bartłomiej Krupa
Developer, Brand24
Visibility

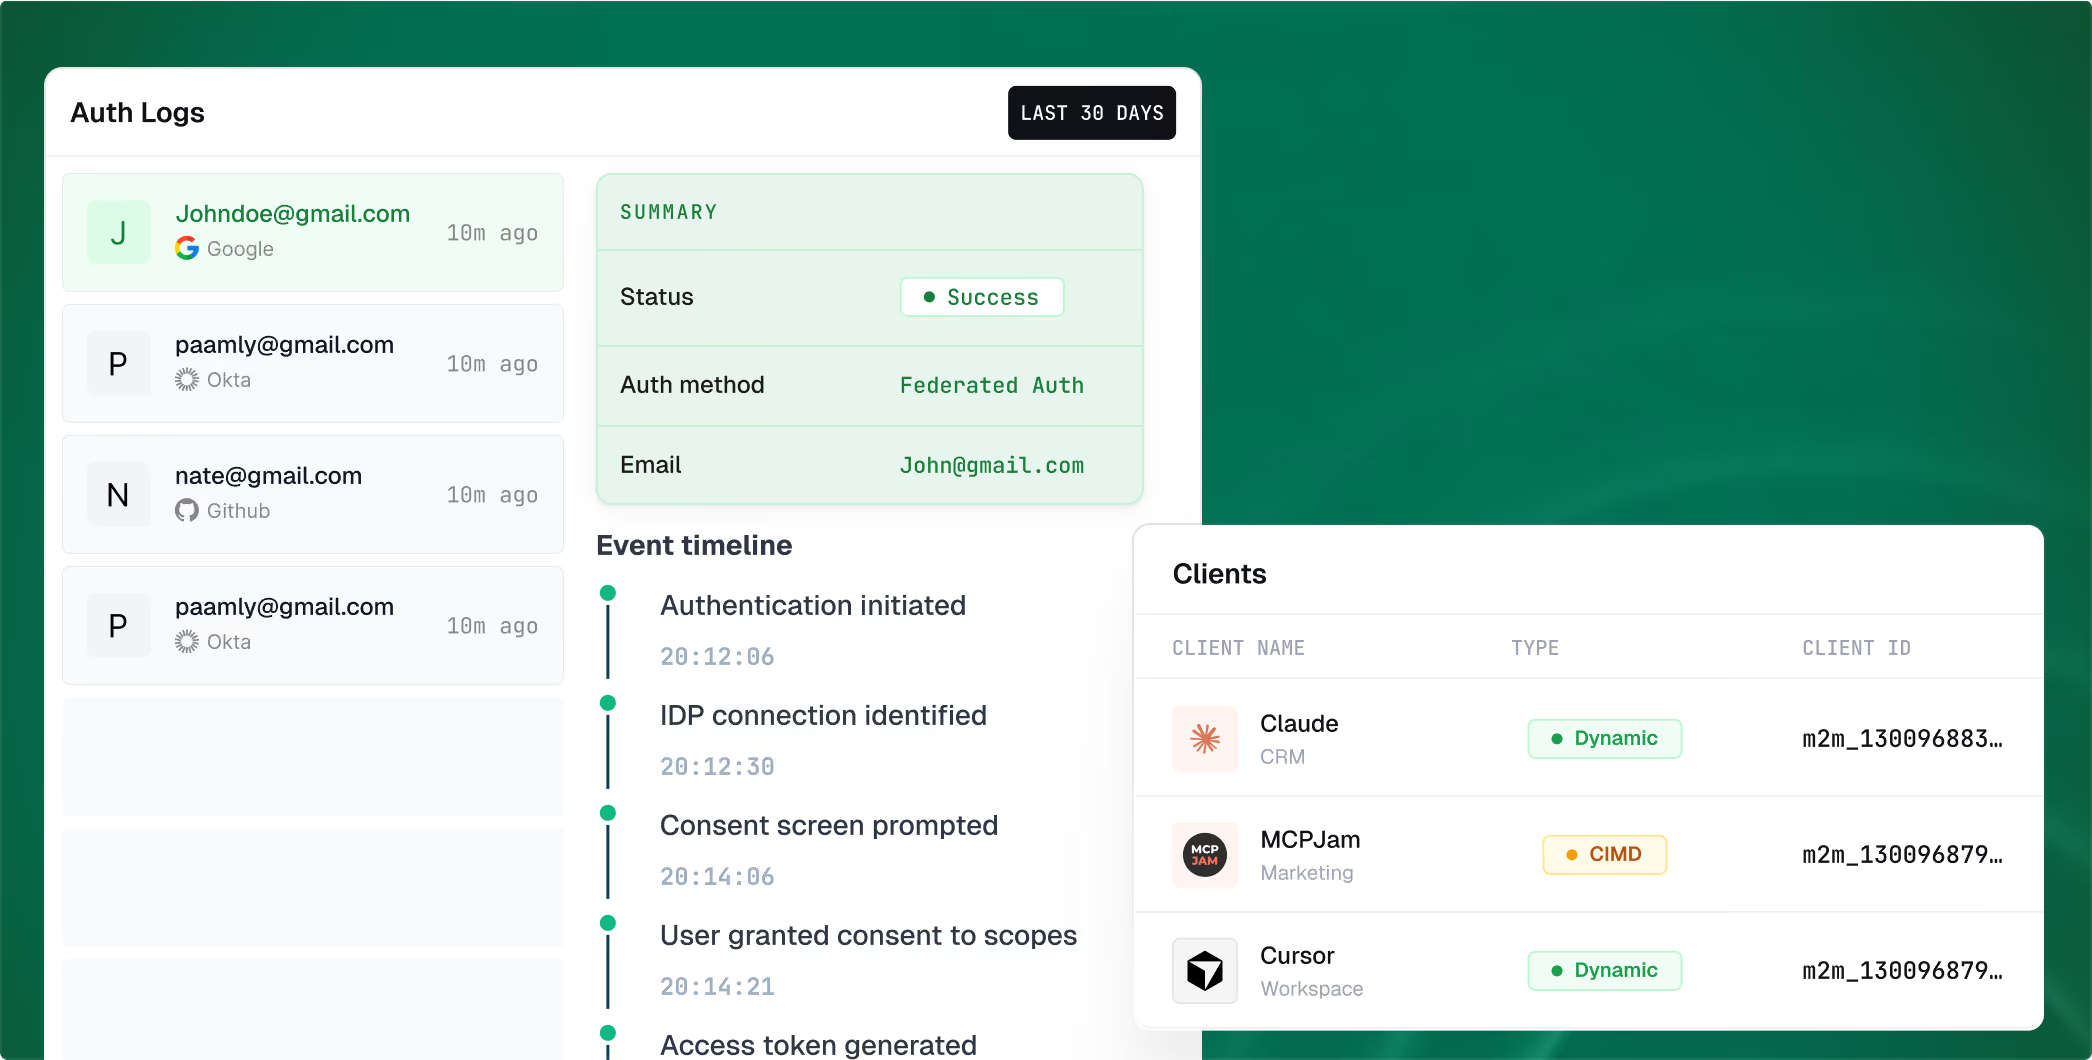
See every client connecting.
And every event.

Which clients are connecting, how often, and the full event trail for every auth request.
01
Client registry

Every MCP client that connects — Dynamic, CIMD, or pre-registered. Call frequency per client.

02
Per-request event timeline

Full chain per auth request: who, what method, consent granted, token issued.

02
Stream to your SIEM

Forward auth events to Datadog, Splunk, or any SIEM. API access on all plans.

Log streaming
Any  SIEM
Log streaming
Where it runs

Two reasons
teams add MCP auth.

Publish on Claude, ChatGPT, and Cursor
Users add your server from the app directory. Consent, client registration, and scoped tokens — handled.
Power your internal agents
Agents and automated workflows call your server with scoped OAuth credentials. No API key sprawl. No shared secrets.
SECURITY & COMPLIANCE

The auth layer
any security team can sign off on.

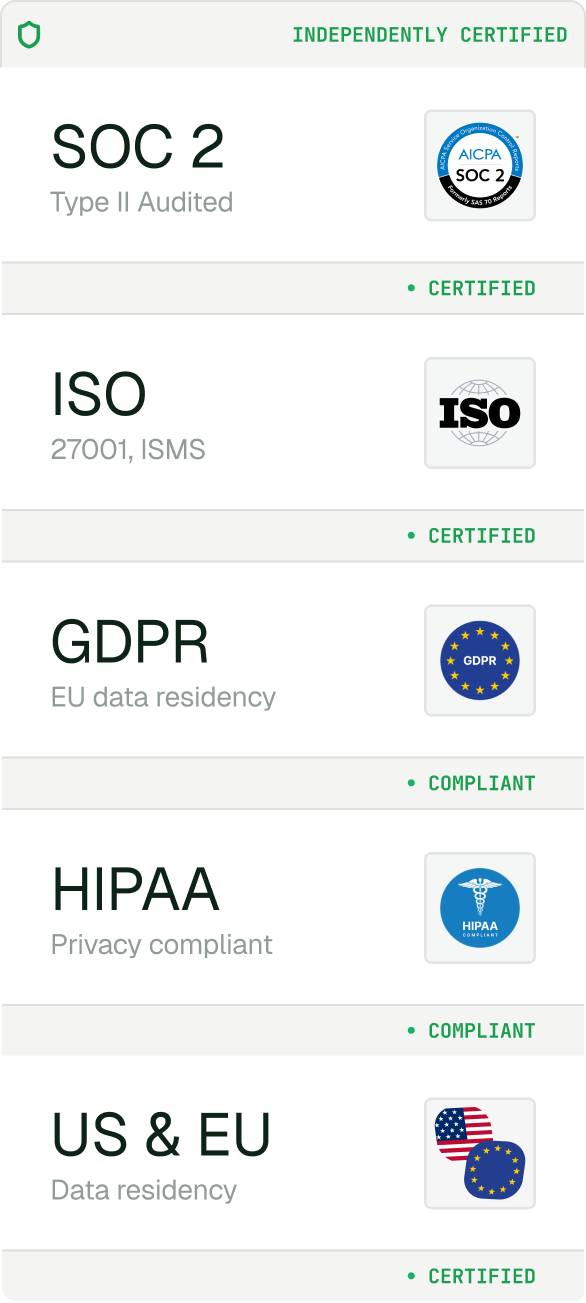
Every token logged. Every consent tracked. Hosting options that fit your posture.
01
Policy before execution

CIMD prevents phishing at registration. Servers verify the client's actual domain — not just what it claims.

02
Validate anywhere

RS256-signed JWTs validate at Kong, AWS API GW, or Cloudflare Workers without a live Scalekit call.

03
Consent you control

Token lifetime, scopes, and user consent managed per MCP server — revoke any grant in one click.

Hosting options
Cloud managed
VPC deployment
On-prem

Your MCP server is one afternoon
from production auth.

Free plan available. Most teams are in production the same day.